The list of affected organizations reads like a who’s who of major international businesses and institutions.
Among the names identified were CNN, Fox News, Zoom, the BBC, HSBC, Equifax, Salesforce, Peacock, IKEA, NPR, the ASPCA, and Invisalign.
However, there is an important distinction: The discovery involved malicious scripts embedded in website code. It does not establish that hackers successfully penetrated the internal computer networks or private databases of every organization identified.

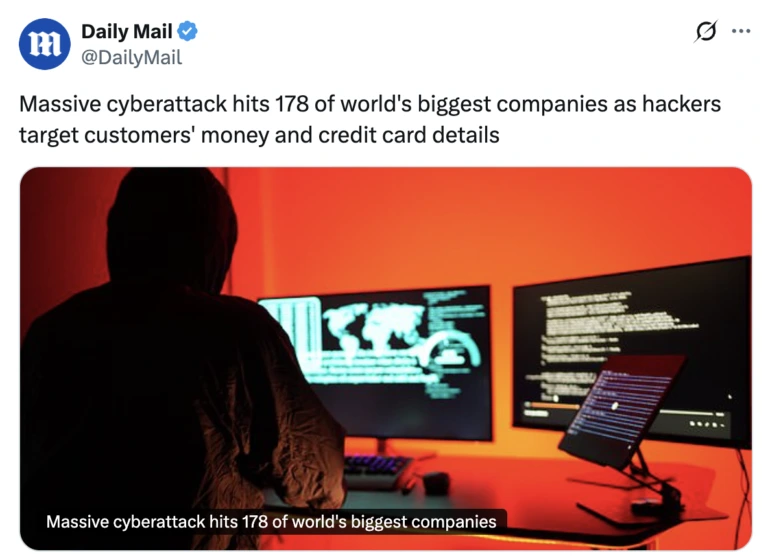
Nevertheless, the scale of the incident raises serious questions about the security of the third-party services that major companies depend upon to conduct business online.
Hackers Exploit a Trusted Technology Provider
At the center of the incident was Optimizely, a software provider that helps businesses experiment with website designs, improve digital experiences, and test different features.
Organizations use these services to make their websites more effective and user-friendly. But in this case, a vulnerability in the company’s technology provided attackers with an opportunity to inject malicious JavaScript into customer projects.
Optimizely acknowledged the security issue, confirming that attackers had exploited a vulnerability to introduce unauthorized code.
The company subsequently reported that it had addressed the vulnerability and removed the malicious injections.
The method used by the criminals was particularly concerning because it allowed them to take advantage of websites that visitors already trusted.
Instead of relying on suspicious links, deceptive advertisements, or fraudulent websites, the attackers found a way to distribute their malicious instructions through legitimate online destinations.
For ordinary internet users, that distinction makes the incident especially troubling.
A visitor could potentially encounter the malicious code simply by opening an affected webpage, without knowingly downloading a suspicious file or clicking on an unfamiliar link.
Three Different Ways Hackers Could Profit From the Attack
Researchers identified several malicious capabilities within the compromised scripts, suggesting the operation was designed to generate financial rewards through multiple avenues.
One component targeted cryptocurrency transactions.
The malicious software could interfere with legitimate wallet addresses, substituting addresses controlled by the attackers. Consequently, someone attempting to send cryptocurrency to another individual could unknowingly transfer the funds directly to a criminal-controlled wallet instead.
Once a cryptocurrency transaction is completed, recovering the money can be extremely difficult, making this particularly attractive to cybercriminals.
The researchers also identified functionality designed to capture payment card information.
This component targeted financial details entered into certain website forms, potentially allowing criminals to collect credit card numbers and other sensitive payment information.
There was, however, an important limitation.
According to the researchers, payment fields hosted separately by providers such as Stripe and Adyen were outside the reach of this particular card-stealing component.
That distinction means the malicious software did not necessarily have access to every payment transaction conducted on affected websites.
The third capability involved exploiting security weaknesses affecting Apple’s mobile devices.
Researchers identified functionality designed to take advantage of vulnerabilities in iPhones and iPads, potentially exposing devices running susceptible software versions to additional security risks.
The combination of cryptocurrency theft, payment information collection, and mobile-device exploitation suggests the criminals were pursuing several opportunities to monetize the compromised websites.
Thousands of Dollars in Cryptocurrency Already Traced
The financial implications of the operation remain unclear.
Researchers monitoring cryptocurrency activity identified approximately $7,040 in digital currency received by wallets controlled by the attackers as of Monday afternoon.
That amount represents an early snapshot of the activity investigators were able to trace. It should not be interpreted as the total amount stolen or the full financial damage caused by the operation.
The number of individuals whose credit card information may have been captured also remains unknown.
Likewise, investigators have not established how many iPhones or iPads were successfully compromised through the malicious scripts.
The absence of a confirmed victim count makes it difficult to determine the full scope of the operation.
What is already clear, however, is that the criminals managed to exploit a software provider whose technology was connected to a substantial number of recognizable organizations.
Attack Took Place November 16 — What Internet Users Should Do Now
The attack unfolded on Monday, November 16.
Report URI identified the infected files after examining 1,611 Optimizely scripts, ultimately uncovering 188 maliciously modified files.
For consumers who visited affected websites that day, cybersecurity precautions are particularly important.
Anyone who entered credit or debit card information into a potentially affected website should carefully examine recent account activity and watch for transactions they do not recognize.
Contacting the financial institution immediately is advisable if suspicious charges appear. Consumers may also want to request a replacement card if they believe their payment information was exposed.
Those who conducted cryptocurrency transactions should independently verify that their funds reached the intended wallet address. Anyone who suspects an address was substituted should investigate the transaction using the relevant blockchain records.
Apple device owners should also make sure their iPhones and iPads are running the latest available software updates. Installing security patches can help protect against vulnerabilities that criminals may attempt to exploit.
The incident serves as another reminder that online security is not determined solely by the website displayed in a browser’s address bar.
Major companies can invest heavily in protecting their own networks, but their customers may still face risks when outside technology providers become compromised.
And that is perhaps the most alarming lesson from this attack: Cybercriminals do not always need to defeat the security systems of major corporations directly. Sometimes, finding a weakness in a trusted service operating behind the scenes is enough to put millions of potential visitors in their crosshairs.

